Kenya’s data protection framework must keep pace with AI, government platforms and global data flows
Kenya's ODPC has spent six years building its enforcement capacity. AI, offshore data processing and connected government systems are exposing the legal and institutional demands facing its next commissioner.

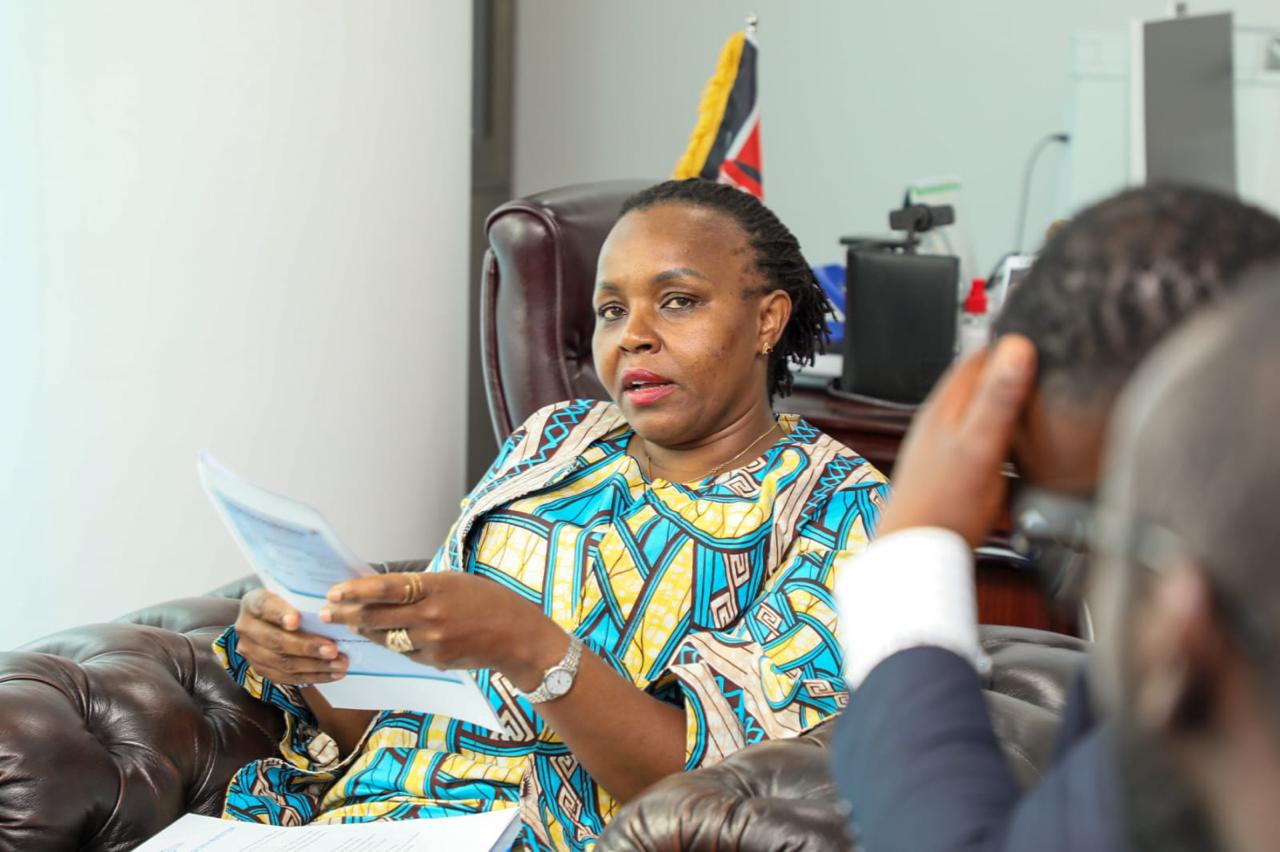
Kenya’s data protection regulator is confronting a growing problem: the country’s digital economy is developing faster than some of the legal and investigative mechanisms designed to protect the personal information behind it.
Artificial intelligence is entering financial services, businesses are adopting offshore software and cloud platforms, and government agencies are working towards interconnected digital systems. Each development creates new demands on the Office of the Data Protection Commissioner (ODPC), whose authority was established under the Data Protection Act, 2019.
The law gave Kenya a framework for regulating how organisations collect, process, store and share personal information. Six years into its implementation, however, the regulator is confronting questions that extend beyond the legislation’s original provisions.
Immaculate Kassait, who is leaving office as Kenya’s first Data Commissioner, says the Act requires amendments covering artificial intelligence, sensitive personal information, penalties and data governance. She also wants the ODPC to receive stronger powers to investigate organisations operating outside Kenya and more time to determine complaints.

Her assessment comes as President William Ruto nominates Lydia Sitienei Chelagat, the Communications Authority of Kenya’s Director of Legal Services, to succeed her. Chelagat’s nomination was announced on 10 November 2026 and forwarded to the National Assembly for consideration.
The transition comes as several parts of the Kenyan economy are developing their own requirements for handling personal information, leaving the incoming commissioner with an increasingly complex regulatory environment.
AI regulation is developing across different institutions
One of the clearest indications of the regulatory challenge is the growing use of artificial intelligence in financial services.
Kassait argues that the Data Protection Act does not adequately address contemporary AI applications. Its provisions primarily address the technology through automated decision-making, while businesses now use AI in activities involving customer profiling, data analysis and other forms of personal information processing.
Developments in financial regulation demonstrate how the issue is already reaching sector regulators.
On 7 November 2026, TechTrendsKE reported on Kenya’s 2026 Non-Deposit Taking Credit Providers Regulations, which introduce requirements covering AI-driven lending decisions. Regulation 60 addresses explainability, disclosure of AI involvement, human oversight, discriminatory bias, model accuracy and accountability.
The requirements apply within the digital credit regulatory framework. They do not constitute a comprehensive replacement for data protection legislation, but they demonstrate the growing need to regulate how automated systems use information to make decisions affecting consumers.
A lender using an AI model to assess a borrower’s creditworthiness, for example, must consider both the financial regulatory requirements governing lending decisions and the data protection obligations associated with processing customer information.
The ODPC has also been developing guidance for businesses using offshore AI services. Draft guidance reported by TechTrendsKE in August 2026 addresses safeguards for transferring personal information to foreign AI providers, including contractual protections, data processing agreements and assessments of destination-country safeguards.
The proposals reflect a practical problem facing Kenyan businesses. Outsourcing AI processing does not transfer responsibility for protecting customer information to the technology provider.
Companies uploading customer records to external AI platforms must consider where the information is processed, the legal basis for its use and the safeguards governing access and retention.
The challenge for the ODPC is to ensure that existing data protection obligations remain effective across these different arrangements. Kassait’s proposed legislative reforms suggest that administrative guidance alone may not address every emerging application of the technology.
Global technology companies expose the limits of domestic enforcement
The location of personal information has become another operational concern for the regulator.
Kassait says the Data Protection Act has extraterritorial application, allowing the ODPC to investigate organisations outside Kenya when they process the personal information of Kenyan data subjects within the law’s scope.
However, the regulator does not have mutual legal assistance powers, making it difficult to obtain evidence held in other jurisdictions.
She cites the Business Registration Services data breach investigation as an example. The ODPC had to seek assistance from foreign data protection authorities, including European regulators, to identify the controller involved.
The problem is not necessarily whether Kenya has legal jurisdiction over a particular organisation. It is whether the regulator can obtain the information needed to investigate that organisation and establish responsibility for a breach.
This has implications for businesses that rely on international cloud infrastructure, foreign software vendors and global digital platforms. Personal information belonging to Kenyan customers may be processed or stored in jurisdictions where the ODPC cannot independently access the relevant evidence.
The regulator’s proposed reform agenda therefore extends beyond increasing penalties. Kassait wants legislative changes that would strengthen cooperation with foreign authorities and improve access to information held outside the country.
The distinction between regulating cross-border data transfers and investigating foreign-based organisations is important. The former concerns the conditions under which personal information can be transferred and protected. The latter concerns the practical powers available when a regulator needs evidence from another jurisdiction.
Kenya needs an effective framework for both.
Government digital infrastructure adds another layer of responsibility
The expansion of government digital services creates a separate set of data protection concerns.
The government has been considering ways to commercialise anonymised datasets held through eCitizen and other public systems. A proposal reported by TechTrendsKE in June 2026 envisaged at least 1,000 datasets over five years, with an estimated development and operating cost of KSh396 million.
The proposed marketplace would exclude personal identifiers such as names, phone numbers and national identification numbers. Its intended datasets include information relating to business registration, government service demand, immigration applications, vehicle registrations and land transactions.
The government has also been pursuing a unified platform to connect public institutions through secure application programming interfaces and an enterprise system. A September 2026 report by TechTrendsKE said the initiative would support interoperability between government systems and the use of AI agents in public service delivery.
These developments expand the importance of data governance beyond individual government databases. Information collected by one institution may become accessible to other agencies through shared infrastructure, creating additional requirements for access controls, authorisation, audit trails and accountability.
Kassait acknowledges that government institutions still have considerable work to do on compliance.
She identifies enforcement actions against the Ministry of Agriculture and Migori County Assembly, rejecting the perception that the ODPC has concentrated its attention on private companies. However, she admits that public-sector compliance remains below the level the regulator wants to achieve.
The commercial use of government datasets and the integration of public systems make that admission particularly relevant. Removing direct identifiers does not, by itself, resolve every privacy risk associated with combining datasets or allowing third parties to use them.
The incoming commissioner will therefore inherit a regulatory responsibility that extends into the design and operation of public digital infrastructure.
Worldcoin exposed the consequences of weak biometric safeguards
Kenya’s experience with Worldcoin provides a concrete example of the risks associated with collecting sensitive personal information before the regulatory implications of a business model have been adequately addressed.
The company, through Tools for Humanity, collected biometric information from participants using iris-scanning devices. The exercise attracted regulatory scrutiny over its purpose, the legal basis for processing the information and the use of financial incentives to encourage participation.
Kassait says the ODPC engaged Worldcoin before its intervention became publicly visible. She disputes suggestions that the regulator acted too late, explaining that the company repeatedly changed its position during discussions about its processing activities.
One concern involved Worldcoin’s reliance on legitimate interest as a lawful basis for processing personal information. Kassait questioned whether that justification was appropriate when participants were being enrolled for a service that was supposedly going to be available in the future.
The dispute subsequently went through the courts. A May 2025 High Court outcome addressed the absence of a mandatory Data Protection Impact Assessment and the use of financial incentives in obtaining consent.
In January 2026, TechTrendsKE reported that the ODPC had confirmed the deletion of biometric information collected from Kenyans by Tools for Humanity.
The case demonstrates the difficulty of supervising technology companies whose services depend on collecting information that cannot readily be replaced following exposure or misuse. Unlike a compromised password, an individual’s iris remains a permanent biometric identifier.
It also provides a measure of the consequences of regulatory intervention. The ODPC eventually secured a corrective outcome, although the case required legal proceedings and subsequent action.
Six years of enforcement have changed corporate compliance
Kassait leaves behind an institution that has developed a substantial enforcement record.
She says the ODPC has handled more than 13,000 complaints, issued 459 determinations and taken 206 enforcement and penalty notice actions. The regulator has also registered approximately 28,000 data controllers and processors.
These figures describe the scale of the institution’s activities, although they represent different stages of regulatory work. A complaint does not necessarily result in a determination, while an enforcement notice and a penalty notice are not equivalent to a completed payment or compensation award.
Earlier TechTrendsKE reporting provides some historical context. An April 2025 analysis examining enforcement activity reported 51 determinations in 2024 and average penalties of approximately KSh522,308. Some penalties exceeded KSh1 million.
The same analysis found that 94.3 per cent of the cases it examined involved private entities, compared with 5.7 per cent involving public institutions. That finding provides a historical snapshot of the cases examined rather than a definitive breakdown of all ODPC enforcement activity.
Separate reporting by TechTrendsKE in January 2026 said more than KSh30 million had been paid to individuals in 2025 following data protection violations.
These payments represent compensation to affected individuals and should not be confused with penalties collected by the regulator.
Kassait says the ODPC has also moved the data protection discussion beyond specialist legal and technology circles. She estimates that almost 70 per cent of people did not know about data protection when the regulator began its work, while awareness has improved considerably since then.
However, she says organisations must progress beyond understanding the law. They need to audit their systems, establish where personal information is stored, develop governance policies and put mechanisms in place to respond to data breaches.
She identifies the financial sector as one of the areas approaching greater compliance maturity, partly because customer trust is central to its operations.
Digital lenders provide a useful illustration of the remaining challenges. TechTrendsKE’s February 2026 reporting documented concerns involving the misuse of borrowers’ contact lists, harassment of third parties and aggressive debt collection practices.
These cases show why registration and awareness cannot serve as the final measures of compliance. Organisations must demonstrate that their actual processing activities, security controls and customer-handling practices meet their legal obligations.
The ODPC also needs more room to investigate
Beyond the law itself, Kassait identifies operational constraints within the regulator.
The ODPC has 90 days to determine complaints, a period she says can be difficult to meet when cases involve complex investigations and large volumes of information. She wants the timeline extended.
She also acknowledges the need for additional institutional capacity as the regulator’s responsibilities grow.
Investigations involving AI systems, biometric information, international cloud providers and interconnected government databases require expertise that extends beyond conventional legal compliance. Digital forensics, cybersecurity, software architecture and international regulatory cooperation all contribute to effective enforcement.
The outgoing commissioner has not presented the proposed reforms as limited to increasing penalties. Her recommendations also cover the expansion of sensitive personal data definitions, including greater attention to political party membership, and a wider scope for data governance.
These changes would affect how organisations identify and manage information that carries additional privacy risks.
Chelagat inherits a regulator with a wider technology mandate
Chelagat’s nomination places the ODPC’s next phase of development within a broader conversation about coordination between Kenya’s regulatory institutions.
Her background as Director of Legal Services at the Communications Authority gives her experience within another institution responsible for overseeing the country’s communications sector. Her nomination process followed 152 applications and the shortlisting of 13 candidates, according to TechTrendsKE’s November reporting.
The Commission on Administrative Justice has also been working with the ODPC on a joint advisory opinion addressing the relationship between access to information and data protection. The collaboration involves consultations, referrals, capacity building and institutional experience-sharing.
That relationship will become relevant as government agencies seek to make more public information accessible while maintaining protections for personal data.
Kassait’s successor will need to manage these competing responsibilities alongside the expansion of AI, international data processing and digital public services. The ODPC’s work is no longer confined to explaining privacy obligations to organisations. It must also determine how those obligations apply when information moves between institutions, across borders and through automated systems.
The Data Protection Act established the legal foundation for that work in 2019. The regulatory demands now confronting Kenya extend well beyond the circumstances in which the law was first implemented.
Go to TECHTRENDSKE.co.ke for more tech and business news from the African continent and across the world.
Follow us on WhatsApp, Telegram, Twitter, and Facebook, or subscribe to our weekly newsletter to ensure you don’t miss out on any future updates. Send tips to editorial@techtrendsmedia.co.ke

